ShadowTrackr

Getting started

Give us a starting point. Watch your attack surface appear.

Paste any domains, URLs, IP addresses and subnets you want monitored. One domain is enough to begin, but every extra starting point gives you a more complete picture. No installation, and a solid picture in about an hour.

14-day free trial. Hosted in Germany, GDPR compliant.

yourcompany.com mail www vpn: CVE found cloud port 3389 open TLS ok dns supplier
Illustration. Red dots are the things to fix right now.

From empty dashboard to full picture in five steps

Each step builds on the one before. Most people finish the first three in a single sitting.

1

Enter a starting point

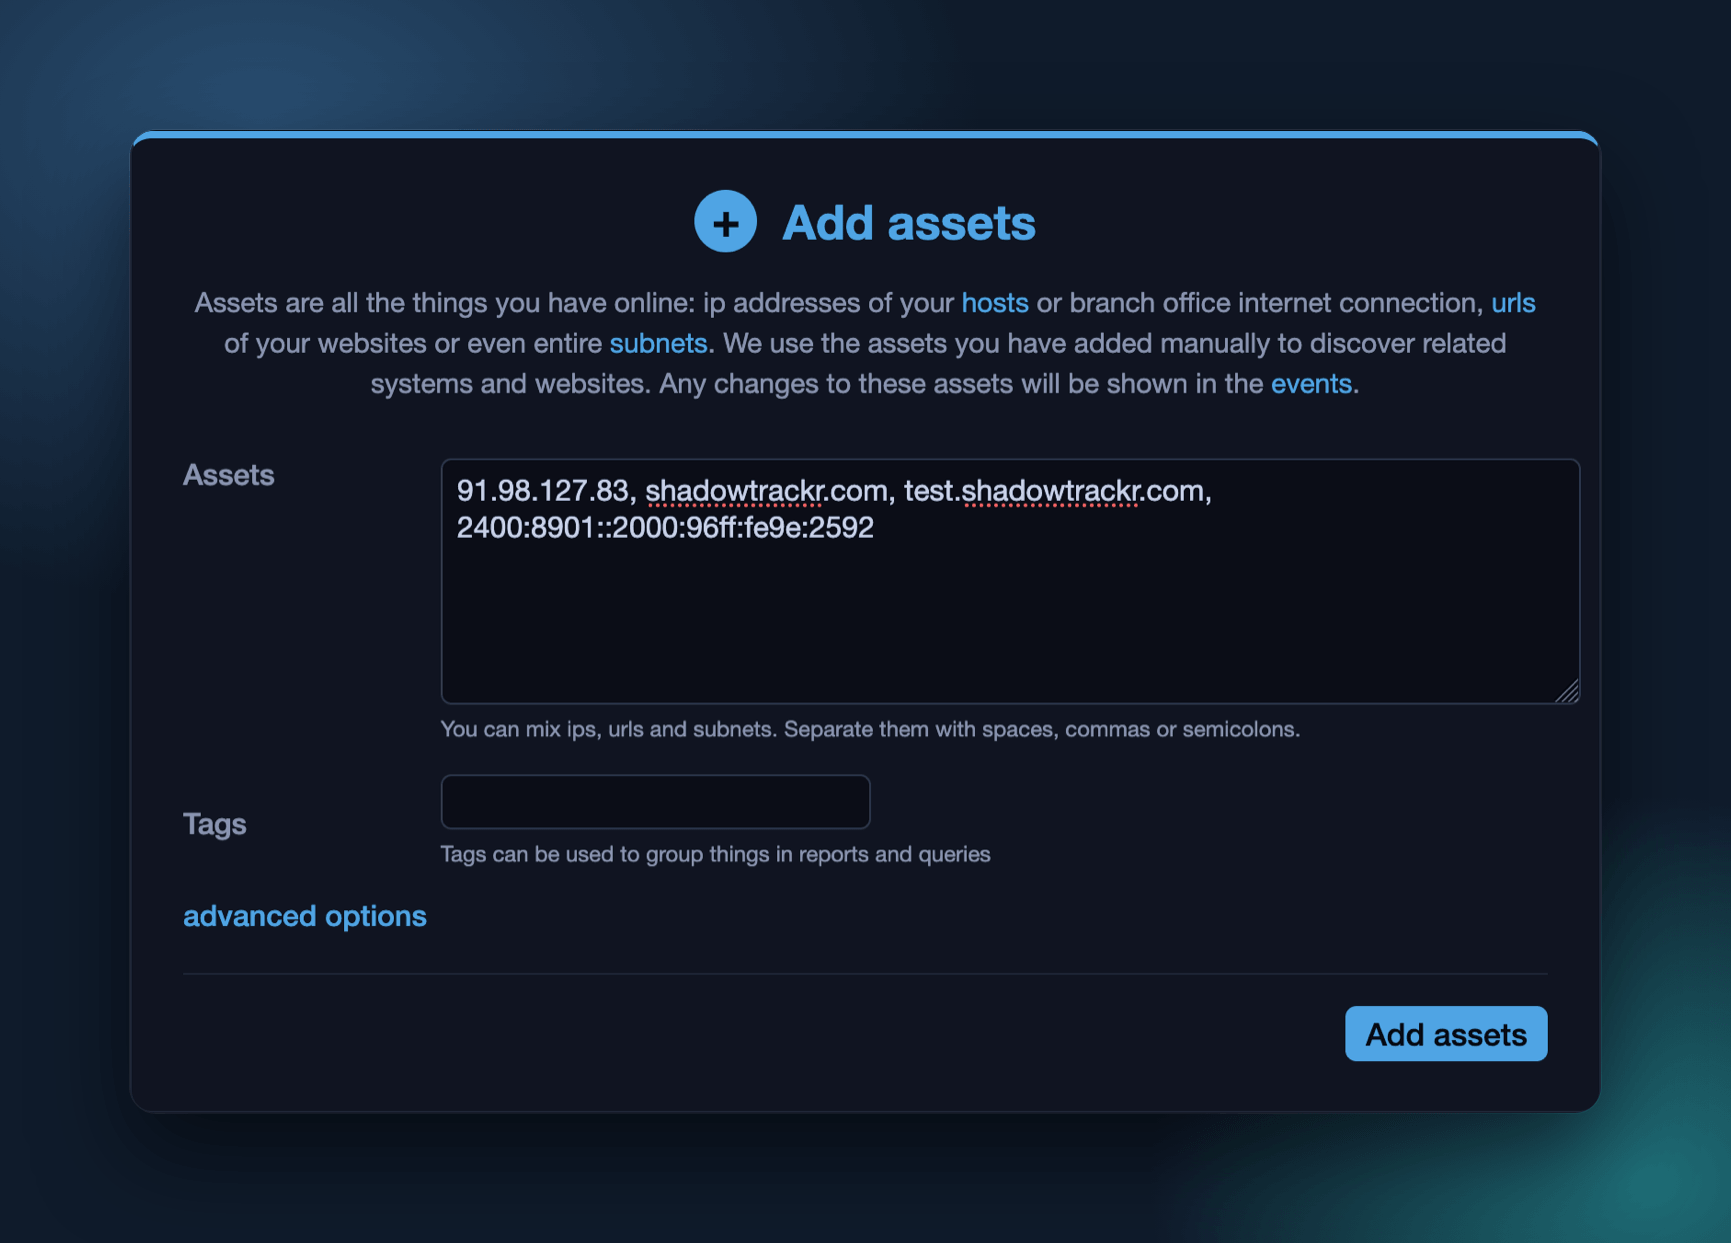
Paste everything you want monitored under Assets: domains, URLs, IP addresses and subnets, one per line or comma-separated, mixed freely. We sort them out. One domain is enough to start, but the more starting points you give, the better the results. Every entry is validated, and internal or unroutable addresses are filtered out. Subnet monitoring is available on premium and enterprise plans.

DomainsIP addressesSubnets
Assets, add field
2

Watch discovery run

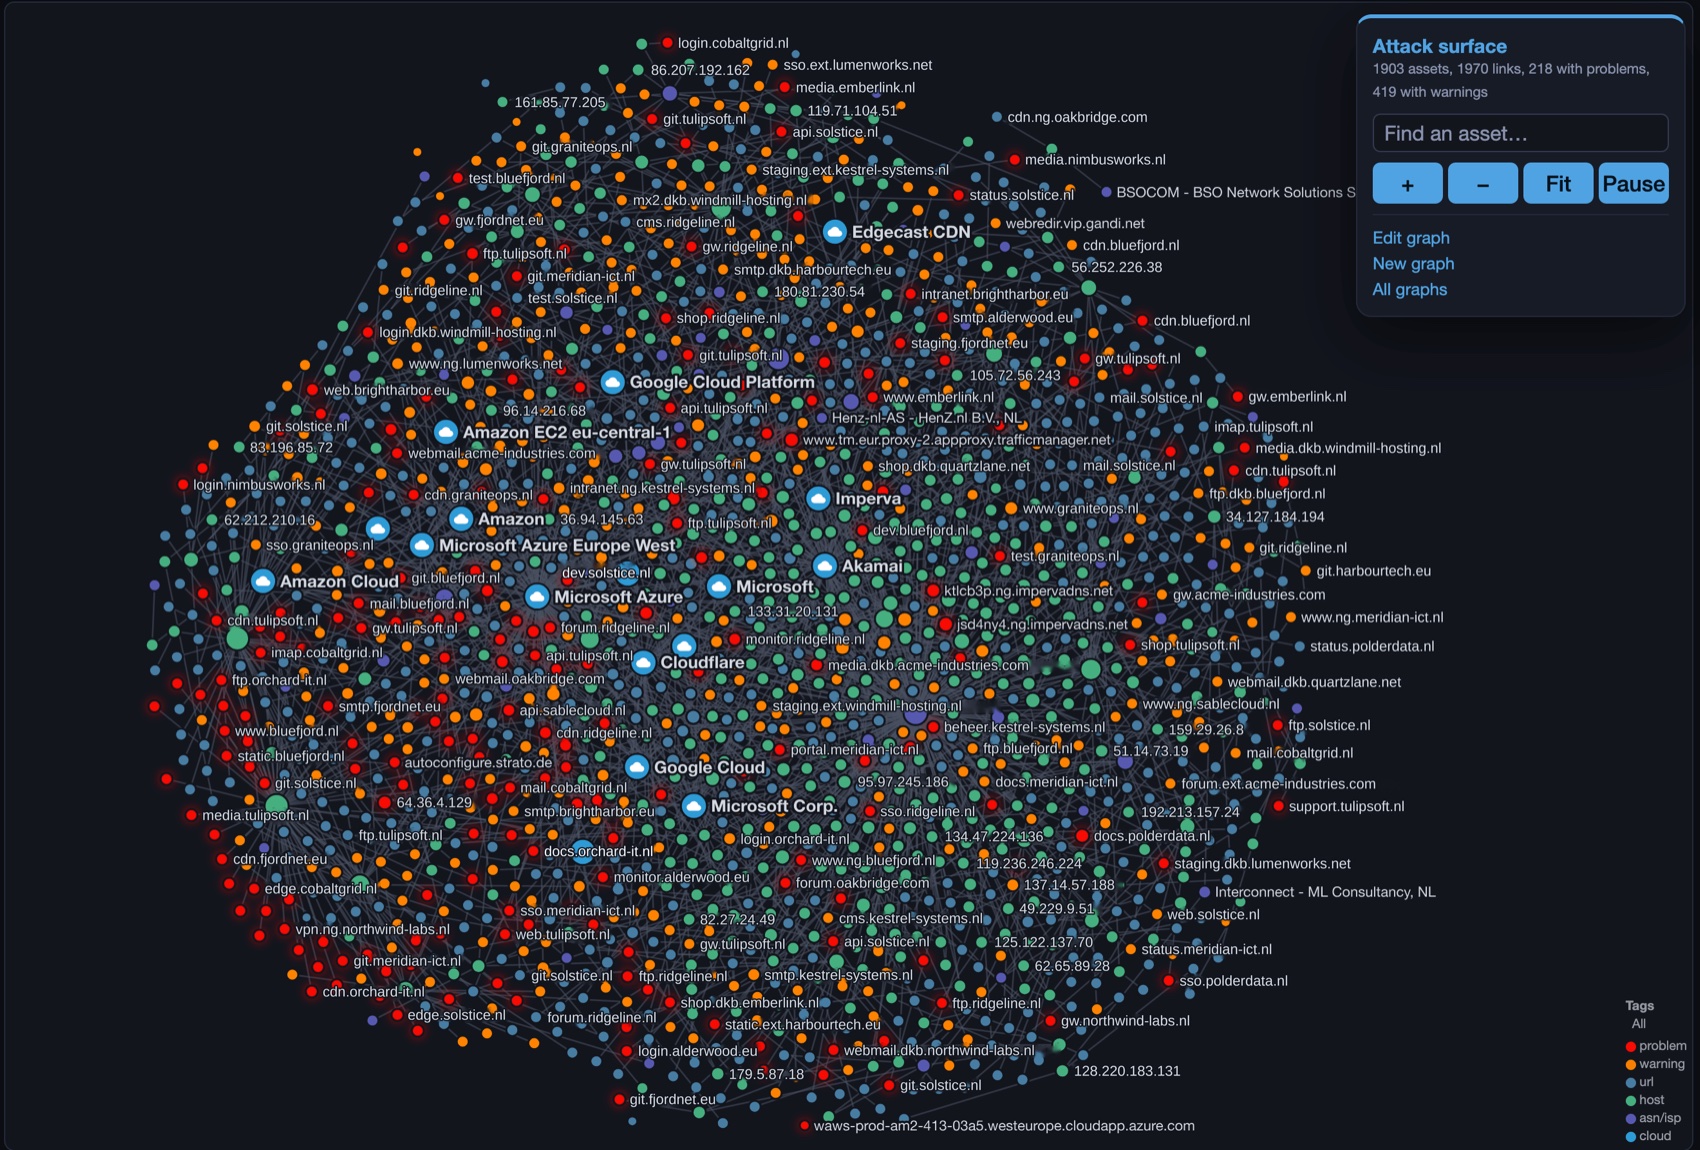
Within minutes, hosts, websites, certificates, DNS records, exposed email addresses, suppliers, vulnerabilities and phishing look-alikes of your domains start to appear. Follow it live on the events timeline. Discovery never stops: most checks repeat daily.

Live timelineAttack surface graph
attack surface graph with red dots
3

Check your suggestions

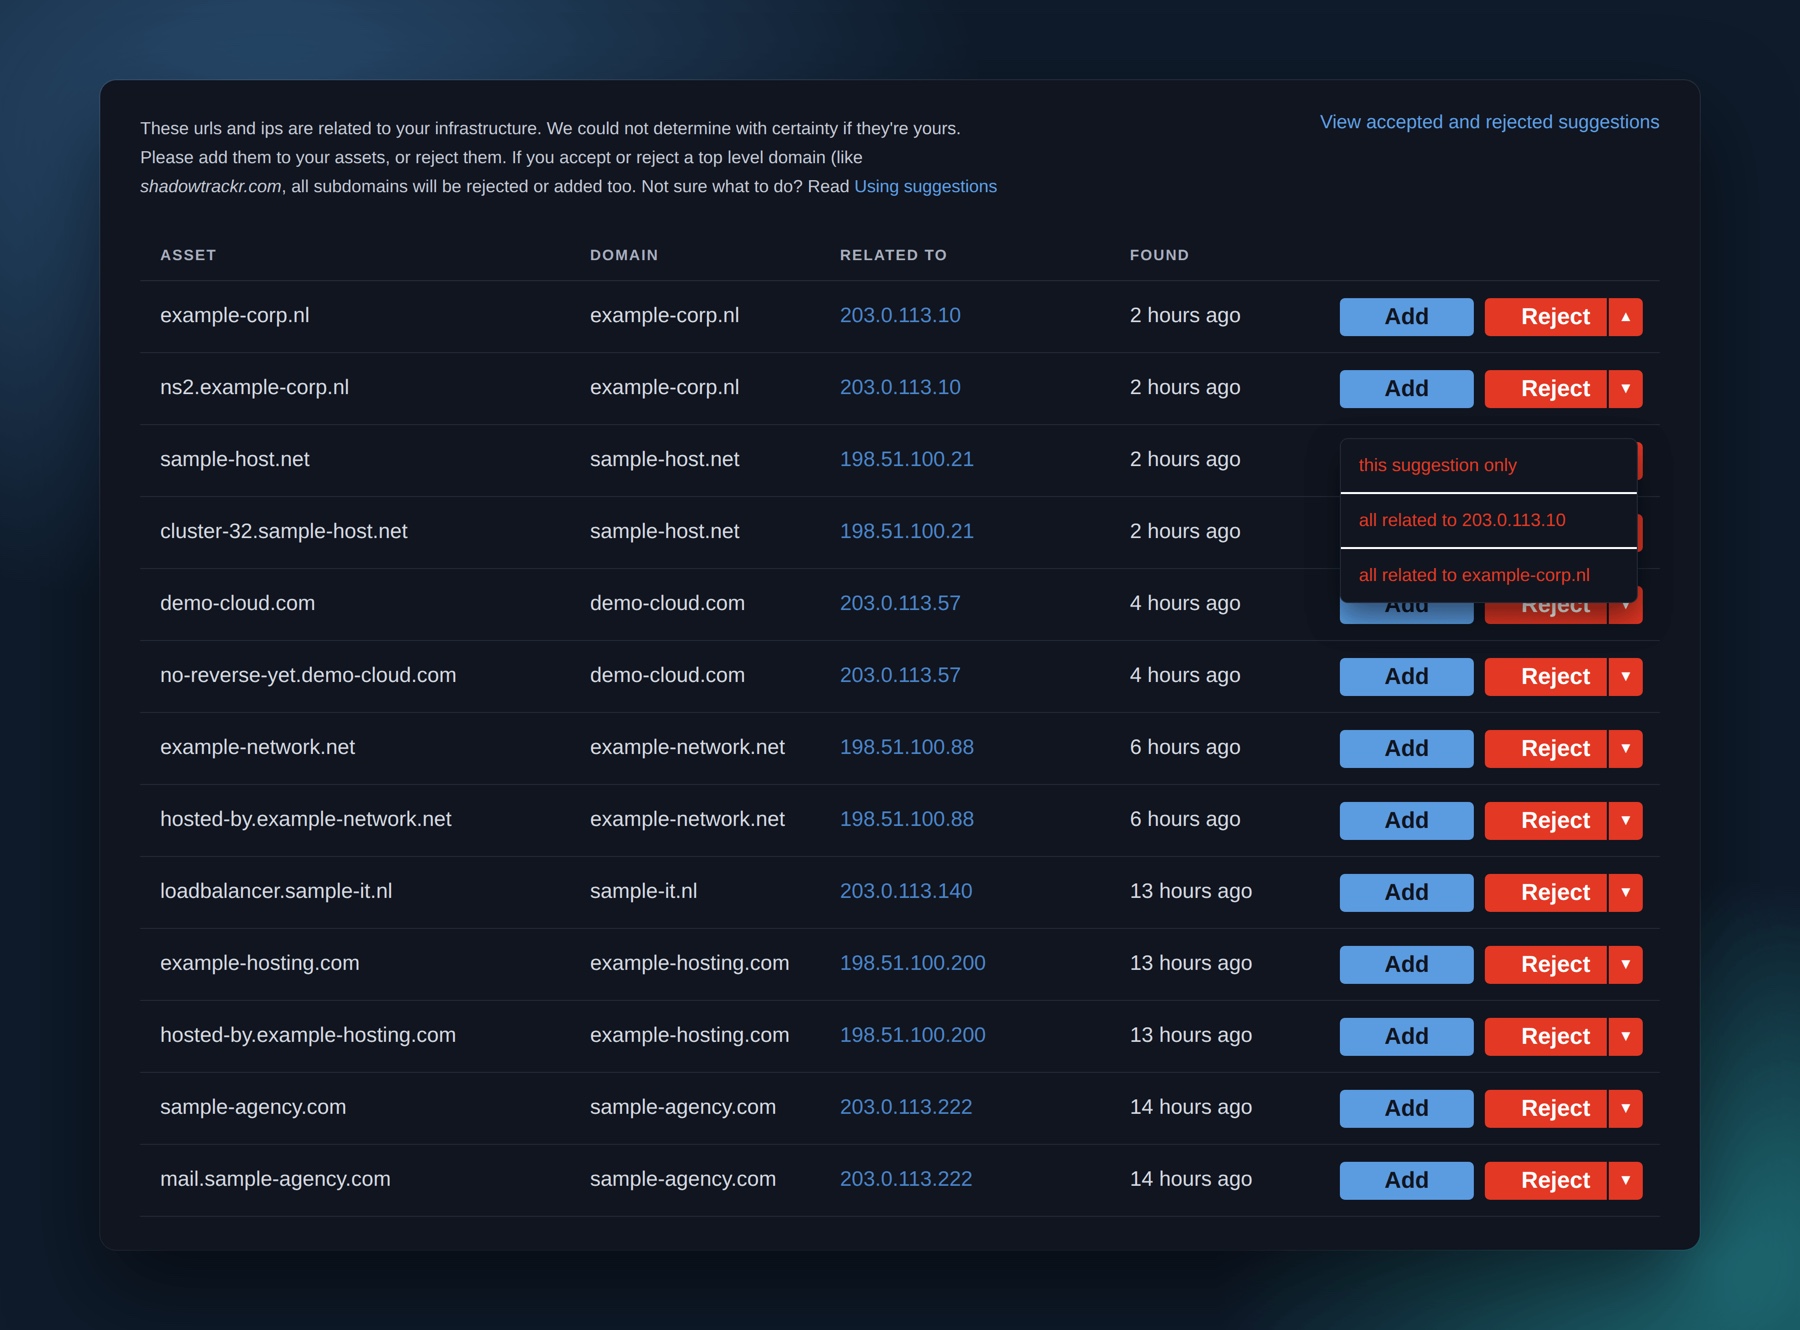
When a scanner can't be certain an asset is yours, such as a neighbour on shared hosting, it asks instead of guessing. Accept or reject with a click. Do this right after your first discovery and the graph stays accurate from then on. How suggestions work.

AcceptReject
Suggestions list
4

Schedule your reports

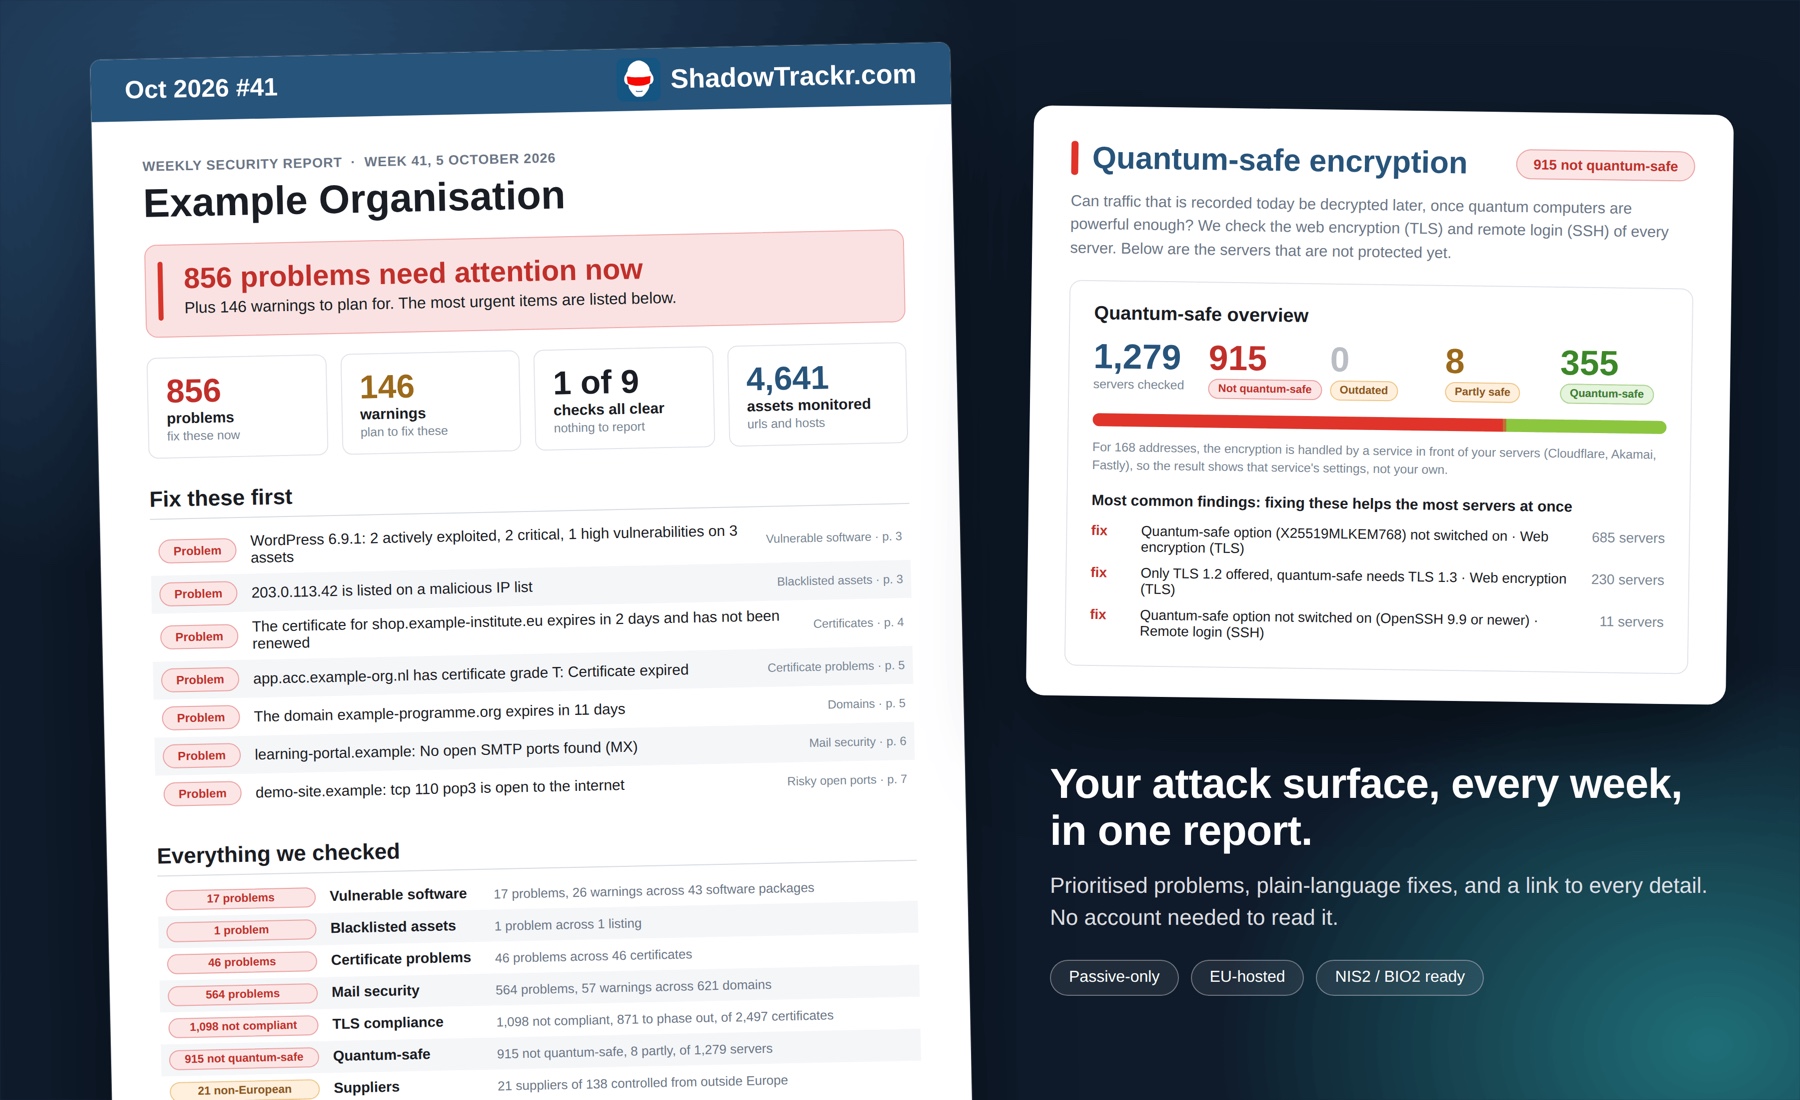
A weekly PDF with your most pressing issues is switched on for every user. Send it to anyone you like, pick more from the Report Library, or write your own with a Splunk-like query language your SOC already knows.

Weekly PDFReport LibraryExcel export
weekly PDF report
5

Let the alerts watch for you

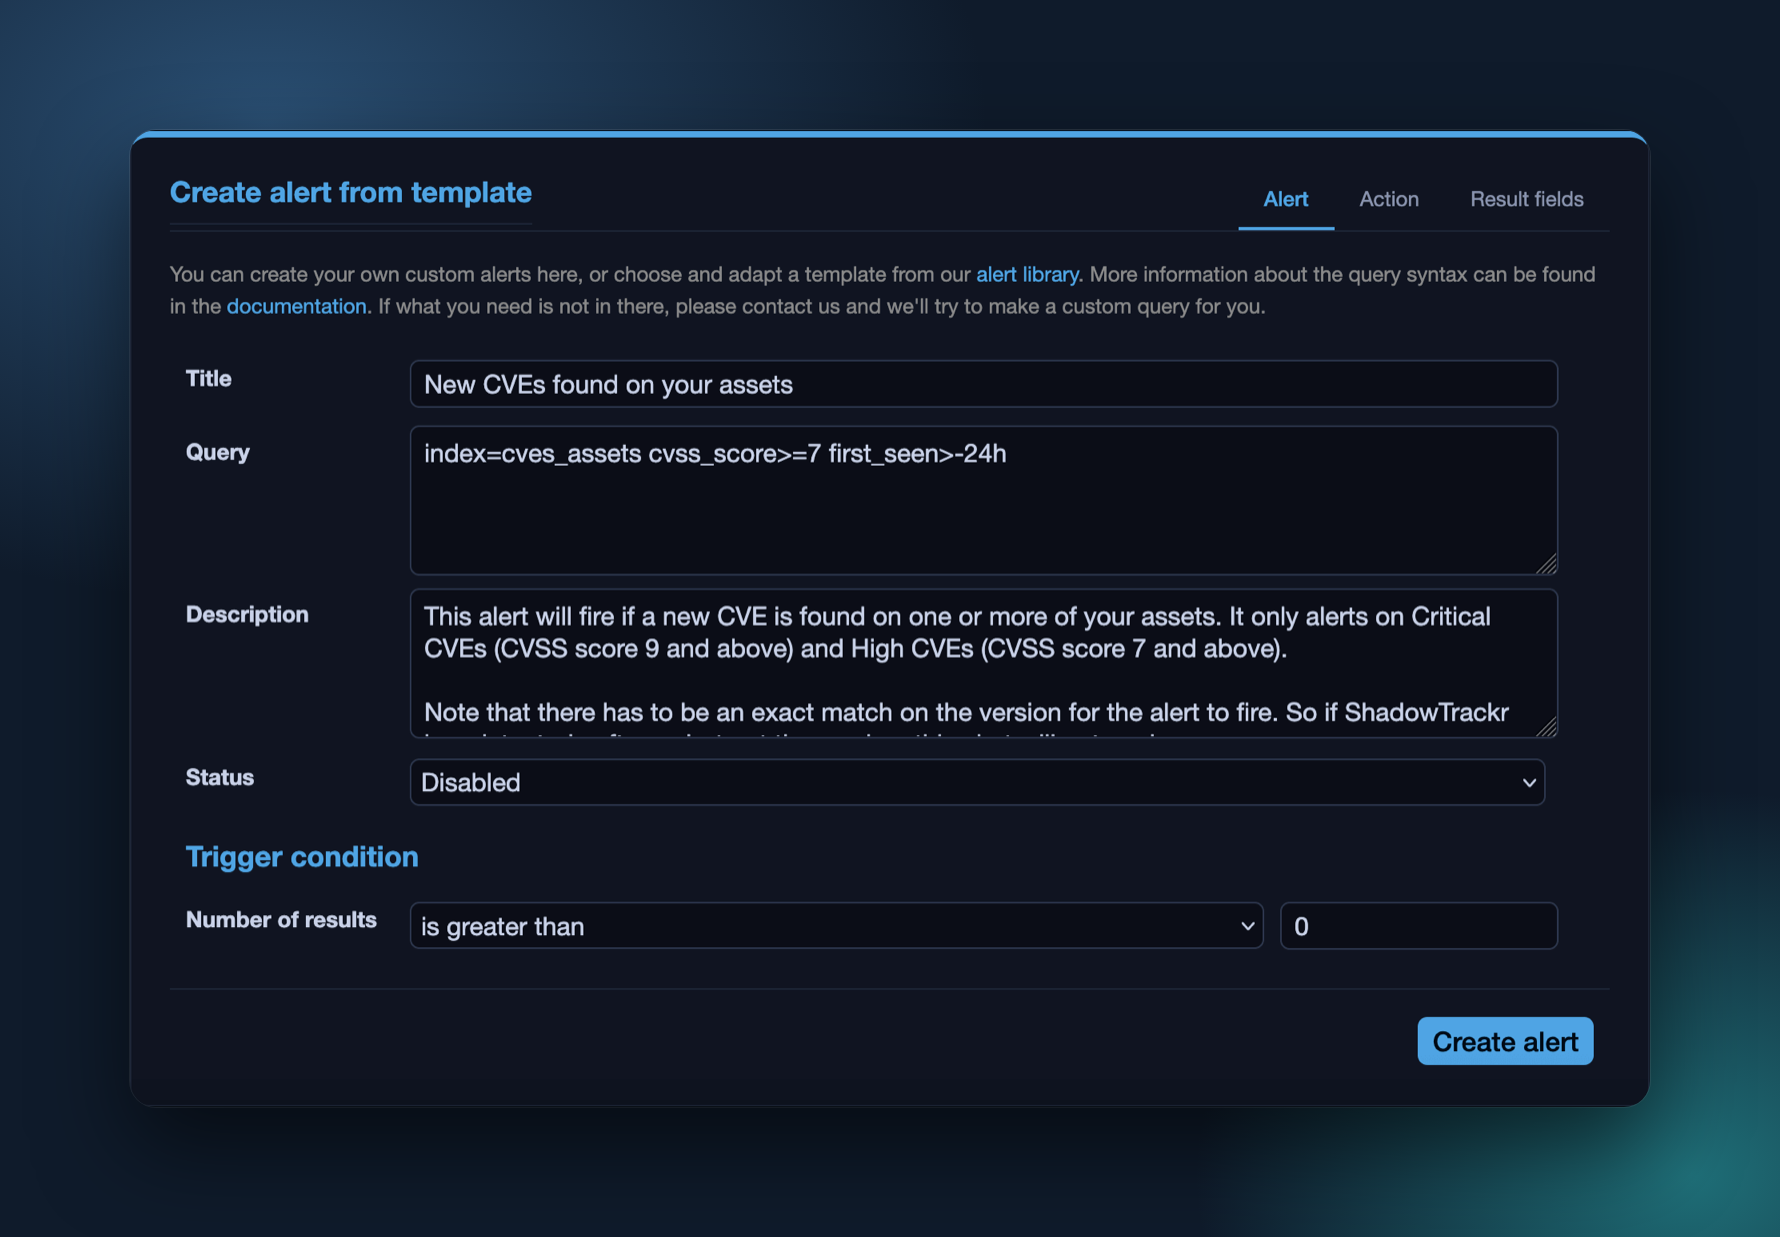
You don't have to keep checking the dashboard. Switch on the alerts that matter and ShadowTrackr tells you the moment something changes. Common starters are already configured for you, the Alert Library has ready-made templates, and "reset user alerts" undoes any experiment.

  • A new CVE hits your software. Know which of your assets are affected, before the news cycle does.
  • It lands on CISA KEV. A vulnerability that is already being exploited in the wild is flagged the moment it is listed.
  • A new Dutch NCSC advisory that applies to what you run.
  • A certificate is about to expire, long before your visitors see a browser warning.
  • Your website is defaced, and you hear it from us instead of from a customer.
  • And many more, or write your own query.
Results arrive by email as Excel, CSV, PDF or JSON, or go to a webhook straight into your own tooling.

Alert LibraryCVEsCISA KEVEmailWebhooks
Alert Library

Keep your attack surface organised

Once discovery is running, shape what you see so the important things stay in front.

Tags

Label your crown jewels, such as mail and remote login servers, and give them their own graph or stricter alerts. Built for accounts with thousands of assets.

Ignore the noise

Ignore URLs or hosts that belong to someone else, even for future subdomains. Think twice though: warning a client about their own exposed server is a feature.

Canary tokens

Plant free tokens from Thinkst and connect them to ShadowTrackr. You hear about it the moment someone touches them. Read how.

Things you probably can't see today

Beyond ports and certificates, the same data answers questions most tools don't ask.

A history that starts the day you do

For most data we keep up to three years of history, counted from when your account became active. Which ports were open last month? When exactly was that vulnerable software exposed? The sooner you start, the more you can look back on when an incident happens.

See your supply chains

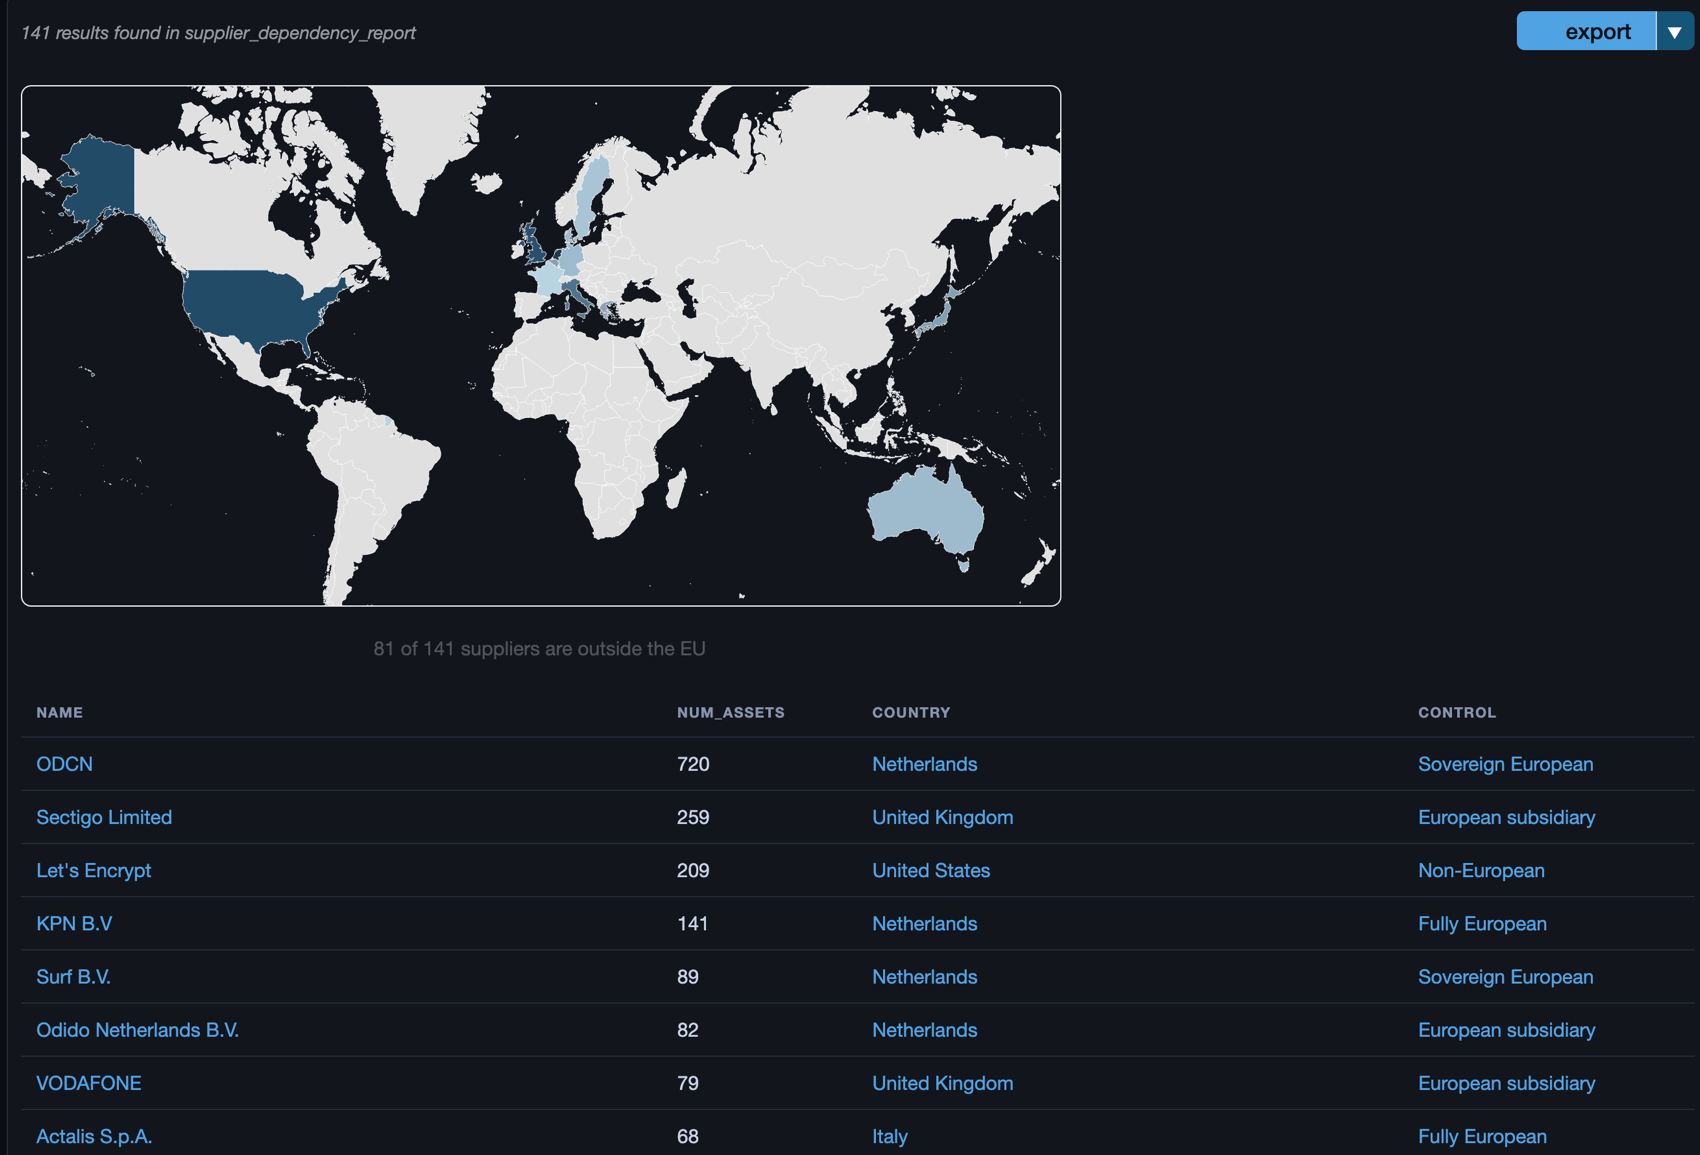
We identify the suppliers behind your software, hosting, certificates and mail, and classify whether each one is controlled in Europe or outside it. Built for NIS2.

Sovereign European
Fully European
European subsidiary
Non-European

Spot phishing look-alikes

Domains that imitate yours are tracked. Block them to stop phishing attacks from reaching your organization, or buy them pre-emptively to protect your brand and your customers too.

Supplier Dependency Report

Keep it useful after day one

Fix problems first

In ShadowTrackr, a problem is something to fix now. A warning matters but can wait. Browse reports and events regularly, and let the weekly report remind you.

Problem: fix now
Warning: fix soon

Be pinged only when it matters

Alerts reach you by email or webhook, and only for the alerts you switch on. Start with the worst ones, so every message stays worth reading.

Plug it into your stack

Pull everything out through the API, available on Business and Enterprise plans (and multi-tenant for MSSPs), or enrich it with other sources.

APISplunkSentinelElasticOpenCTIShodanCensysShadowserver

See your own attack surface today

It takes a list of your domains and IP addresses and a few minutes. Your data stays in the EU.

Start your free trial

14-day free trial. Hosted in Germany, GDPR compliant.

Questions first? Talk to us, check the FAQ or browse the full quick start.